Rewritten October 22, 2026, for NIST SP 800-63A-4: IAL3 proofing must be on-site attended, on devices the provider controls.
This post covers controlled kiosks. For what IAL3 is and how it differs from IAL2, see What Is NIST IAL3?
Now that we have already done a deep dive into NIST IAL 2 (NIST IAL2 Identity Verification An Updated Review of Requirements (opens in a new tab)), we will explore level 3. This will only be at a high level, as a client requested it as an additional method for certain users. Similar to how the government added in-person help for Login.gov at public counters, other businesses may require this feature. For example, if you are a bank and want to achieve IAL3 for wiring a large amount, you could require proofing to be done on-site. In the use case requested, the client wanted agents at its own branch locations to verify sender identities. Another use case is onboarding visitors or employees on their first day. IAL3 is the highest level of assurance provided by NIST and covers the most demanding security cases. NIST publishes a summary of the requirements (IAL3 Summary of Requirements (opens in a new tab)), and many of them match IAL2.
The main difference is how the proofing is delivered. NIST SP 800-63A-4 states that "IAL3 identity proofing SHALL only be delivered as on-site attended" (Proofing Types (opens in a new tab)). The applicant is at a controlled location, using sensors and capture devices that the provider supplies, and a trained proofing agent attends the session. IAL3 can't run on the applicant's own phone or computer. The evidence rules are the same as at IAL2: one piece of SUPERIOR evidence, two pieces of STRONG evidence, or one STRONG and one FAIR. What IAL3 adds is the attended, on-site delivery and the collection and retention of a biometric. Because applicants can't proof from just anywhere, the provider has to bring controlled hardware to where people are. For the government, public counters give national coverage, but most businesses will never have that much physical presence.
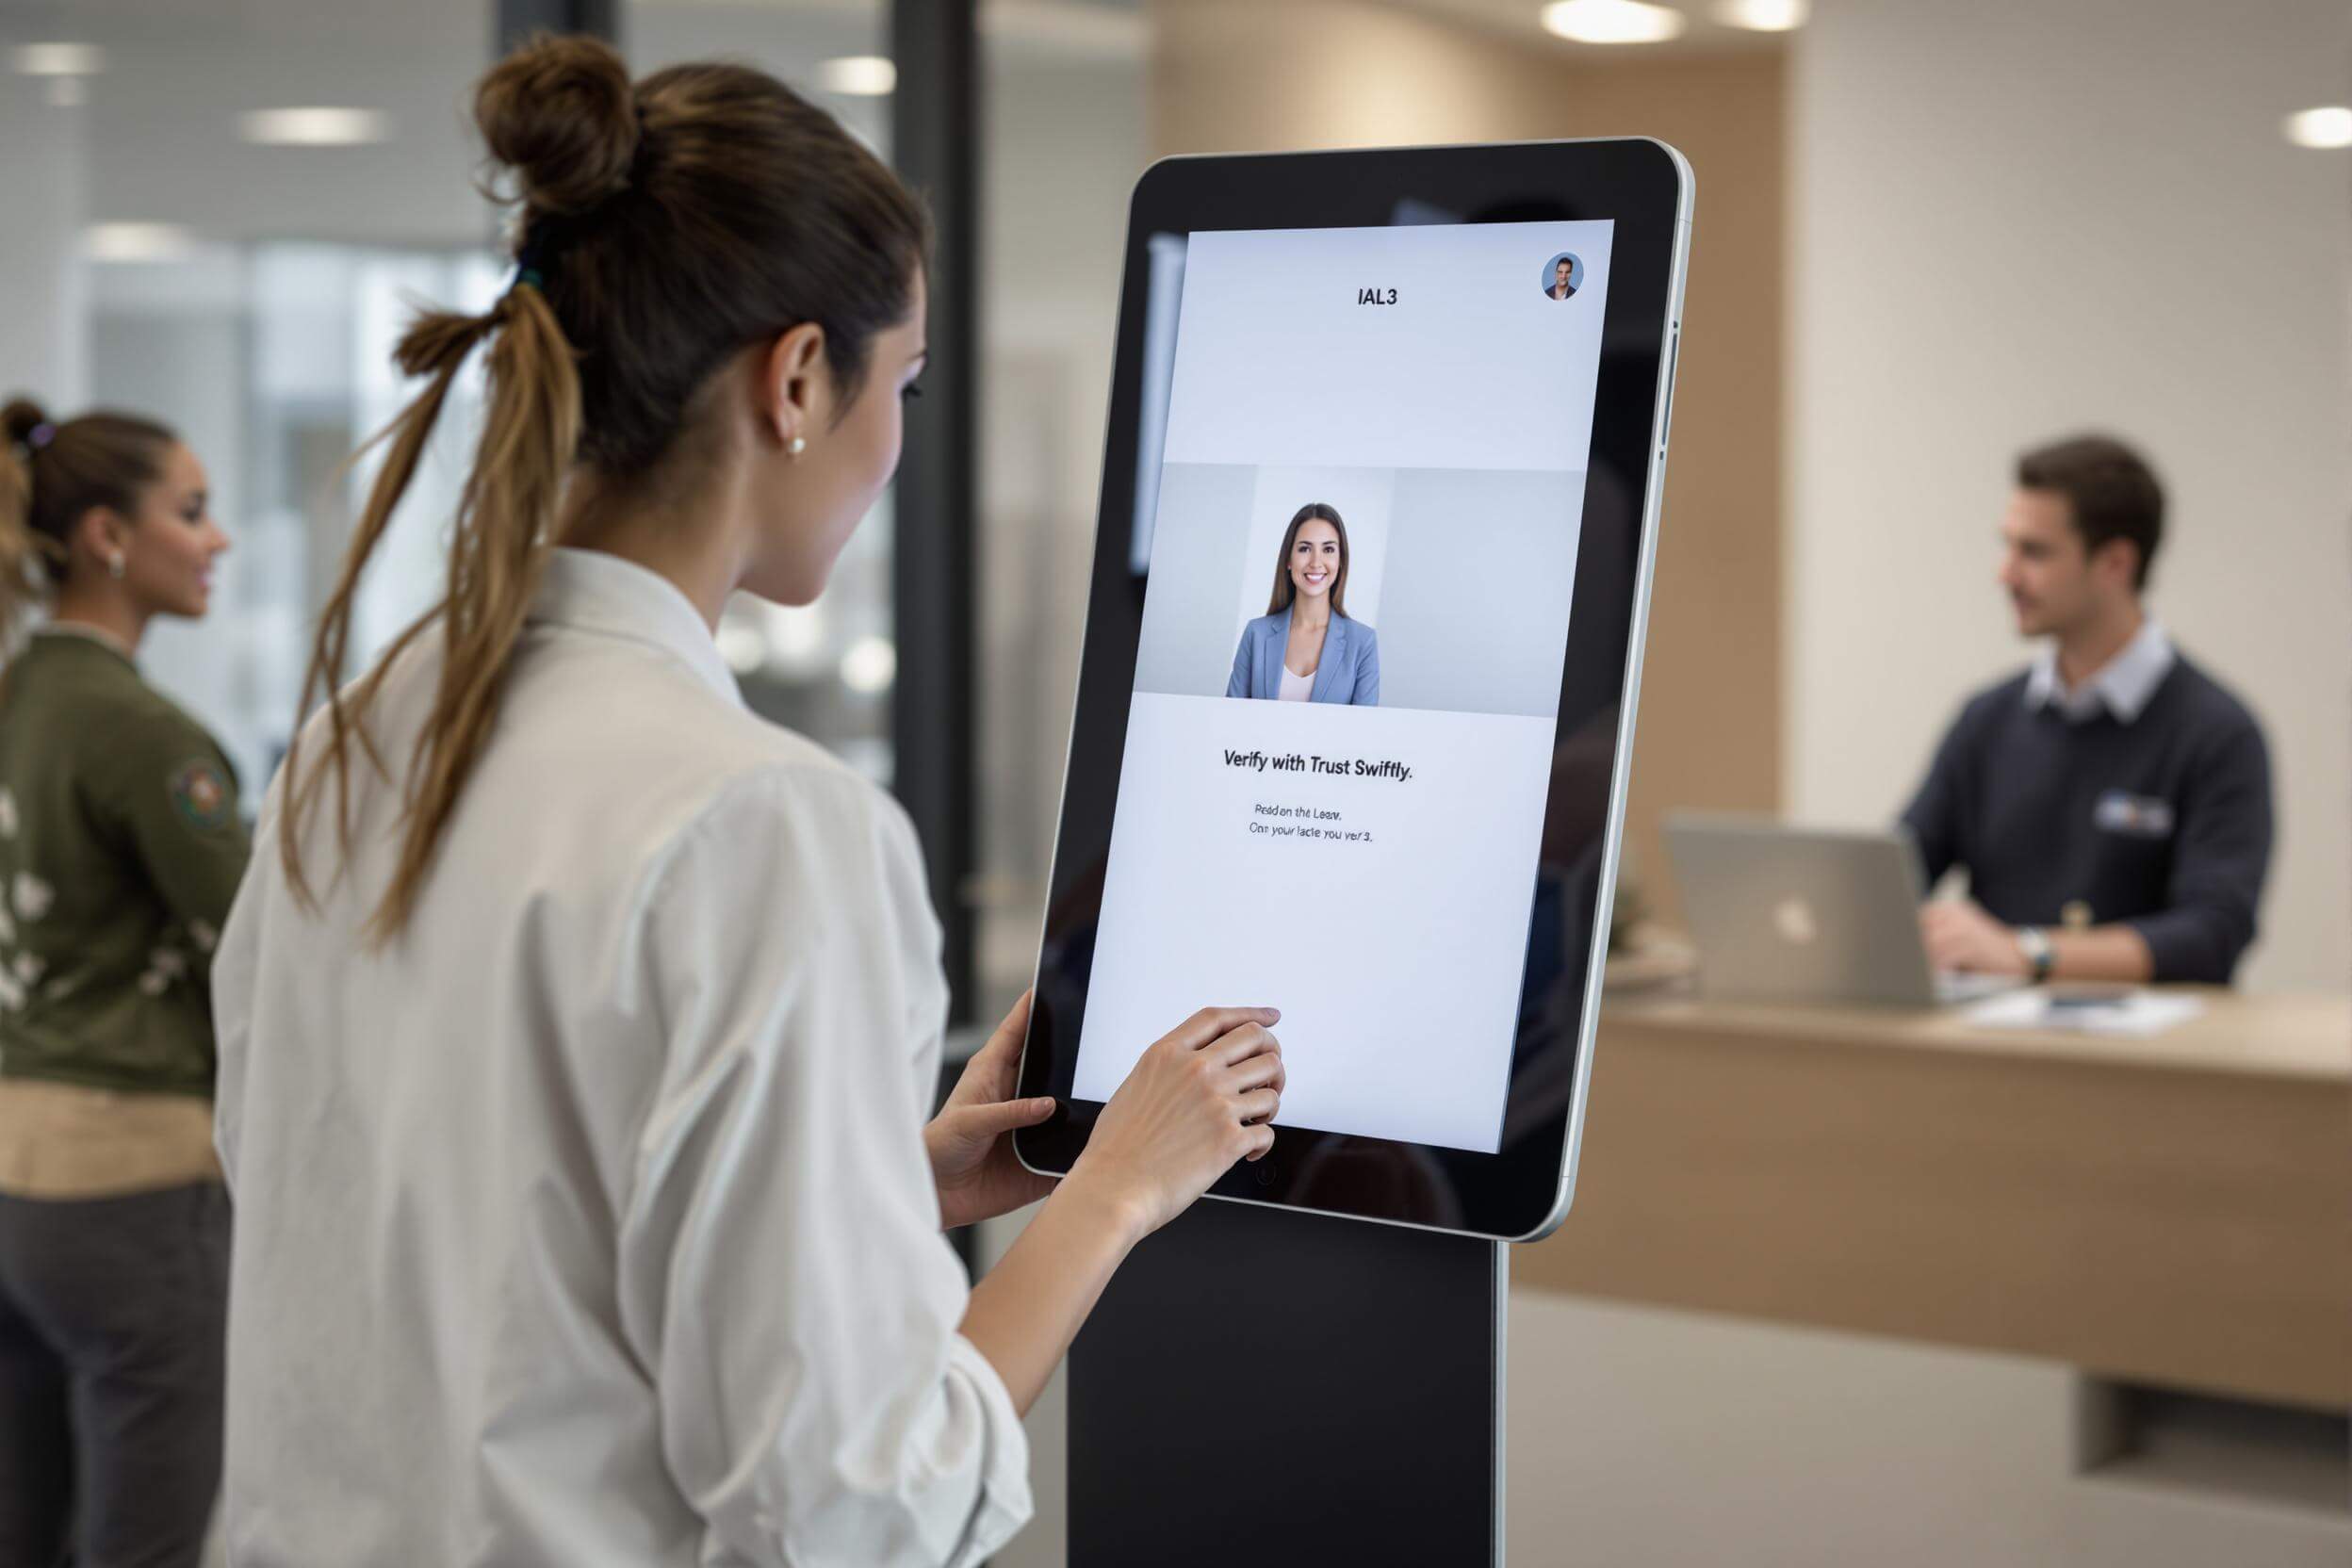
The first plan to achieve IAL3 is a proofing agent at a physical location, similar to how a security guard reviews your information before you are admitted to some offices. Guards already inspect some identity documents, but those checks are woefully inadequate: they miss critical checks that need an internet connection and an application. For IAL3, the steps are much more stringent. The session runs on a Trust Swiftly-controlled kiosk or kit, never on the applicant's own phone or computer, and the agent watches each step as the face and evidence documents are captured. The agent completes the IAL2 checks and then the additional IAL3 steps, such as viewing the biometric capture directly and confirming that the sample comes from the applicant. The main benefit is protection against injection and other biometric attacks, because the capture happens on a locked-down device the provider controls, not on a rooted phone or a feed carrying a generated deepfake. The drawbacks are the cost of an agent who must be physically present and is available only at certain hours, and the risk that the agent is socially engineered during a verification step. A realistic silicone mask could be worn, so agents and detection models must be trained to catch it during the proofing process. If you choose the on-site, in-person attended pathway, document and audit the process, and train agents well to prevent bypasses.
The second approach is on-site attended, kiosk-based proofing, with the agent either co-located or attending through the kiosk. Earlier revisions of the NIST guidelines called this supervised remote identity proofing. The applicant must be present at the kiosk and interacts with the agent through it. A kiosk lets one agent serve many locations, because each session is sent to a central or distributed processing application. For example, if 100 kiosks were distributed nationwide, a few agents could handle the proofing sessions in real time. The agent takes part in the key steps, such as biometric collection and any issue handling, through a live video connection and a liveness check. This saves time, because the agent doesn't have to take possession of the evidence: the applicant places each document in front of the kiosk's camera. The benefits are similar to the first plan, with better cost and scalability. The main risk is the kiosk itself, which has less protection from physical tampering when no one is beside it. Locks, tamper-evident seals and secondary cameras that watch the kiosk all reduce that risk.
Prebuilt kiosk products exist from vendors such as IDEMIA and Thales. Whatever hardware is used, NIST places it under the provider's control: the CSP supplies the sensors and capture devices, and kiosk-based sessions carry their own additional requirements (on-site attended requirements, kiosk-based (opens in a new tab)). At a class level, a device used for IAL3 proofing needs the following controls.
What a Controlled IAL3 Device Needs
Locked down: the device runs only the proofing application, under central device management, so nothing else can be installed or opened.
Provider-controlled and verified: only approved devices that pass integrity checks can start a session.
Tamper-evident: a secured case or mount, with physical and digital tamper protection.
Chip reading: an NFC reader verifies passports and other chip-enabled credentials cryptographically.
Clear capture: a high-quality camera positioned so the agent can see the applicant and each piece of evidence.
Inspected and tracked: the device is inspected after each session and moves under a logged chain of custody.
Deploying Controlled IAL3 Hardware
Sourcing, configuring and auditing this hardware yourself means managing a supply chain, device configuration and physical security. Most security teams do not have the time to become hardware logistics experts.
Trust Swiftly provides the hardware for you. Our fully managed solution means you never source your own components.
On-Premise Kiosks: ready-to-deploy units for your company offices.
IAL3 Kits: secure, shippable hardware for proofing employees at an approved home office.
Full Logistics: we handle shipping, tracking and returns, and maintain the chain of custody.
To get started, deploy our turnkey IAL3 solution. If you need to verify hundreds of employees at once rather than one kiosk at a time, see our model for scaling IAL3 verifications with high-throughput on-site onboarding events.
Once a kiosk or IAL3 Kit is in place, the proofing session runs in Trust Swiftly's application on that device. During the session, a trained agent connects live and reviews each piece of evidence. Central device management keeps every device locked down and lets our team help an applicant through the session. Trust Swiftly can also run checks beyond the IAL3 scope, such as a device check, by transferring the session. With the device, the location and the attending agent all controlled, IAL3 happens at your office or an employee's home office, with no travel, in a process built to resist current fraud techniques such as deepfakes and injection attacks.