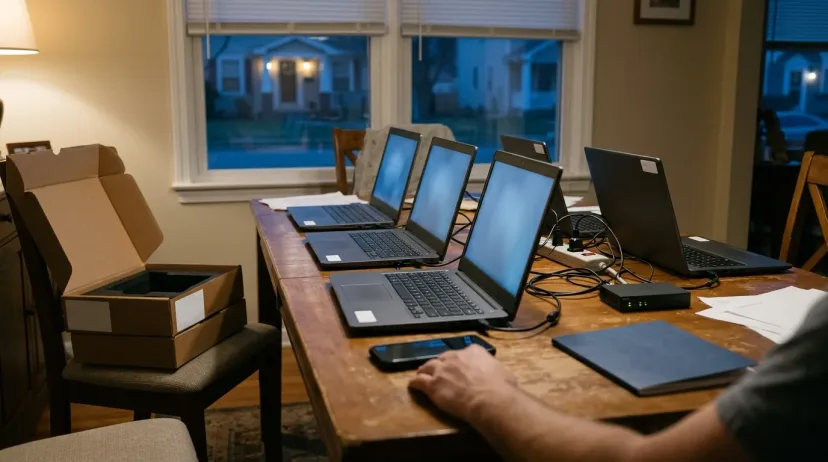
On October 28, 2026, a Gainesville, Virginia man pleaded guilty to conspiracy to commit wire fraud in a scheme that used borrowed U.S. identities to apply for remote jobs. According to the Justice Department, John Allen Kurrle Jr., 62, was employed by a defense contractor for the U.S. government from June to August 2025 and held an active Top Secret clearance with access to sensitive compartmented information (SCI). During that time he allowed foreign individuals to use his identity to apply for remote positions. He also received laptops that victim companies shipped to his home and enabled remote access to them from outside the United States.
As we have documented before, North Korean IT worker schemes depend on people inside the United States. Deepfakes and fully remote fake workers are still common. The more sophisticated groups go further and recruit complicit Americans who lend their real identity and their home, and who show up in person when a check requires it.
That raises a hard question for anyone who relies on identity proofing, including attended NIST IAL3: what can it do when the person in front of the camera is exactly who they say they are, and is helping the fraud anyway?
Complicit identity fraud and IAL3, in brief:
- The pattern: operators pay Americans to lend their real identities, host company laptops and complete live checks themselves, so every identity check passes.
- What IAL3 changes: an attended session on a controlled kit stops stand-ins outright, and turns lending an identity into a documented, personal act that is hard to deny later.
- What it cannot do: no check, IAL3 included, reliably exposes a person who is willing to lie. Pair IAL3 with detection after hire, re-verification at risk events and regular employee attestations.
What the Gainesville case shows
The Justice Department says the applications made with Kurrle's identity, or with a stolen identity, induced nine job offers from U.S. companies. Kurrle is scheduled to be sentenced on January 28, 2027, and faces up to 20 years in prison.
CyberScoop's report on the court records adds detail:
- The scheme spanned at least 88 job applications, and the nine offers carried annual salary ranges of $120,000 to $190,000.
- Kurrle let co-conspirators use his identity and government clearance for prospective sensitive work, "including positions with national security implications."
- A company in Ventura, California hired a co-conspirator under Kurrle's identity as a software engineer on a generative AI project for a component of the U.S. military. It ended the employment, before any work on the military contract, after the person on a video call "did not match Kurrle's age or physical characteristics."
The case holds two lessons. A clearance makes a borrowed identity far more valuable, because it qualifies the applications for roles with more access than an ordinary remote job. And the borrowed identity on its own failed at the first live look at the person: a real name, real documents and a real clearance got through hiring, and a face that did not match ended the job.
That second lesson is why operators increasingly ask the identity owner to handle the live steps. The FBI's October 13, 2026 public service announcement says North Korean IT workers are paying Americans to "appear on camera, participate in job interviews or meetings, verify fraudulent identities," complete urinalysis tests or fingerprint submissions, and keep work devices connected to the internet from their homes, so the setup looks like an ordinary employee working remotely. Some facilitators are paid only for the use of their identities.
Why facilitators are told so little
Operators have little reason to introduce themselves as North Korean government workers. A believable story works better: a freelance gig, a developer overseas who cannot get hired directly, or a version of the outsourcing that many companies do openly. The FBI says operators post fake openings as "freelance gigs with simple requests such as interviewing on someone's behalf," and look for Americans under financial stress who are "more likely to complete facilitation requests without question if paid."
Facilitators are usually financially motivated. Many likely see the arrangement as a way for themselves and someone overseas to make extra money, with the employer still getting its work done. The Justice Department says U.S. facilitators "are paid a fee." When they are caught, a common defense is that they did not authorize their identity to be used that way, or did not know they were doing anything wrong. Sometimes that is partly true: the FBI says operators also use facilitators' identities without permission, or to apply for more jobs than agreed to. According to CyberScoop, Kurrle does not dispute that the scheme likely benefited North Korea, but says he was not aware of the North Korean connection at the time.
Keeping facilitators in the dark also serves the operators. People who believe the arrangement is harmless are easier to recruit and to keep. If more of them understood what facilitators in these cases now face, fewer would sign up.
Why court cases help
Each prosecution gives pause to anyone considering an arrangement like this, and basic research now turns up the consequences. Conspiracy to commit wire fraud carries up to 20 years in prison, and in July 2025 an Arizona woman who hosted a laptop farm for North Korean IT workers was sentenced to 102 months. Every case puts a target on the facilitators still operating and gives them a reason to stop or come forward.
Court cases have limits. They reach the facilitators, while the operators directing the schemes are already moving on to their next victims.
What IAL3 changes for a complicit facilitator
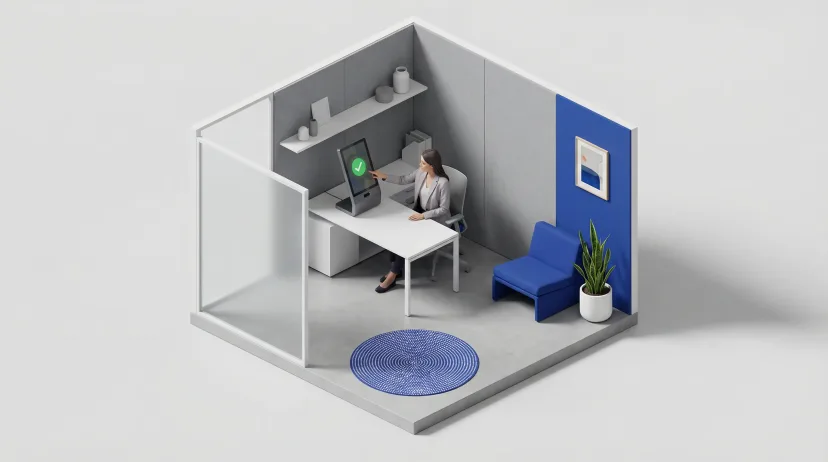
Emailing a photo of an ID and a selfie to someone feels like a small favor. NIST IAL3 is a different experience. The person schedules a session, receives a Trust Swiftly-controlled IAL3 Kit at an approved office or home (or visits an Office Kiosk), presents their own identity documents to the kit, and completes the session while a trained proofing agent attends. NIST SP 800-63A-4 requires IAL3 to be delivered on-site attended, and requires the provider to "collect and retain a biometric sample" to "support account recovery and non-repudiation."
That changes the facilitator's position in three ways:
- Stand-ins fail. The person at the kit must match the identity evidence, and NIST requires the agent to collect the biometric sample from the applicant "and no other source." A stand-in like the person on the Ventura video call would fail at proofing, before any laptop ships. So would anyone using a third person's identity without consent.
- Taking part is documented. A formal, attended process is far more daunting to lie through than an email, and it leaves a record. If a facilitator later says they never agreed to that use of their identity, the record shows they personally completed an attended proofing session for that employer. That is the non-repudiation NIST describes.
- The operator has to explain more. A facilitator asked to complete IAL3 will likely ask the operator why it is needed and how it works. Every extra exchange is a chance for the operator to slip, and for the facilitator to have second thoughts, back out, or report the arrangement. During the session, the agent also watches for signs of coaching or coercion.
What IAL3 cannot do
Many companies hope identity verification, IAL3 included, will be a silver bullet for remote IT worker fraud. No check is. Proofing can flag details that suggest a rented identity, but when a person uses their own real documents, face, phone and address, every value is genuine and every check passes. Identity proofing cannot tell whether a correctly identified person intends to commit fraud, and no other method reliably can: lie detectors are not foolproof either, and there is no dependable way to expose someone who is willing to lie.
Background checks and in-person visits share that limit. A background check validates history, and an office visit confirms who walked through the door. Neither shows what happens to the person's accounts, devices and work afterward. Even requiring someone in the office every day does not solve it, because a person who badges in daily can still pass their credentials, data or the work itself to someone else.
The most thorough vetting belongs to governments, which have long investigation timelines and access to data no private company has. Kurrle held an active Top Secret clearance while he lent his identity. Even governments have a hard time keeping out every bad actor, and catching trained spies is counterintelligence work well beyond what any company can take on. For companies, the realistic goal is active detection.
Detection after onboarding
As threat actors grow more advanced, detection has to keep looking for new signals. The FBI's recommendation is "identity in depth": layered detections, access controls and continuous identity verification throughout employment, with fraud judged on behavioral data rather than easily bypassed rules. In practice:
- Telemetry and AI. Device, network and behavior telemetry, analyzed with AI, can surface scenarios a single check misses, such as remote access tools or hardware on a company laptop, or activity that does not fit the employee's location and routine. Our guide to detecting insider threats and fake IT workers covers the techniques.
- Re-verification at risk events. Verify identity again at role changes, privilege grants, device replacement, account recovery and risk signals, so a handoff after hiring is caught when it matters. Our post on IAL3 retention and re-verification covers the timing.
- Employee attestations. During or after the IAL3 session, and again in every access review, ask employees to confirm a plain statement such as "I attest that my access, my identity and my company devices are used by no one but me." It puts the policy in front of every employee and makes following it their responsibility.
A realistic goal
We hear from many companies that want to solve the fake remote IT worker problem but do not have the capability or resources to do it while running a business. Companies that already do proper due diligence, and have set up processes like IAL3 for high-risk roles, are ahead of the curve. Past a certain level of sophistication, building an impenetrable remote hiring fortress costs more time and money than it saves.
The practical aim is to make every scheme expensive, documented and risky for each person in it, and to keep detecting what gets through. Court cases like this one help the whole industry, but the people directing these schemes are already working on their next targets. Candidate and new-hire identity verification shows how checks at hire, attended IAL3 for privileged roles and re-verification fit together.
Frequently Asked Questions
Can IAL3 identity proofing detect a complicit facilitator?
No, not by itself. IAL3 confirms that the person at the controlled kit matches their identity evidence, and it retains a biometric sample. A facilitator who completes the session with their own documents and face passes. What IAL3 adds is an attended, documented session that stops stand-ins and makes the facilitator's participation hard to deny later. Detection after onboarding has to catch the handoff of work, accounts or devices.
What do facilitators do for North Korean IT workers?
According to the FBI, facilitators are paid to lend their identities, keep company laptops connected from their homes, appear on camera, take part in job interviews or meetings, verify fraudulent identities, and complete urinalysis tests or fingerprint submissions. Some are paid only for the use of their identities.
What did the defense contractor employee plead guilty to in October 2026?
John Allen Kurrle Jr., 62, of Gainesville, Virginia, pleaded guilty on October 28, 2026, to conspiracy to commit wire fraud. The Justice Department says that while he held an active Top Secret clearance, he allowed foreign individuals to use his identity, and to fraudulently use a third person's identity, to apply for remote jobs. He also received company laptops at his home and enabled remote access to them from outside the United States. The applications induced nine job offers. He is scheduled to be sentenced on January 28, 2027, and faces up to 20 years in prison.